 Coance
Risk management for your code
A written, enforced and auditable review policy for your code.
Decide which code needs a careful human review and by whom. Coance checks every pull request against that policy and records who approved each file.
-
Codified
Risk levels and approvers live in coance.yml, versioned and reviewed like code.
-
Enforced
Every pull request is checked against the policy, file by file.
-
Traceable
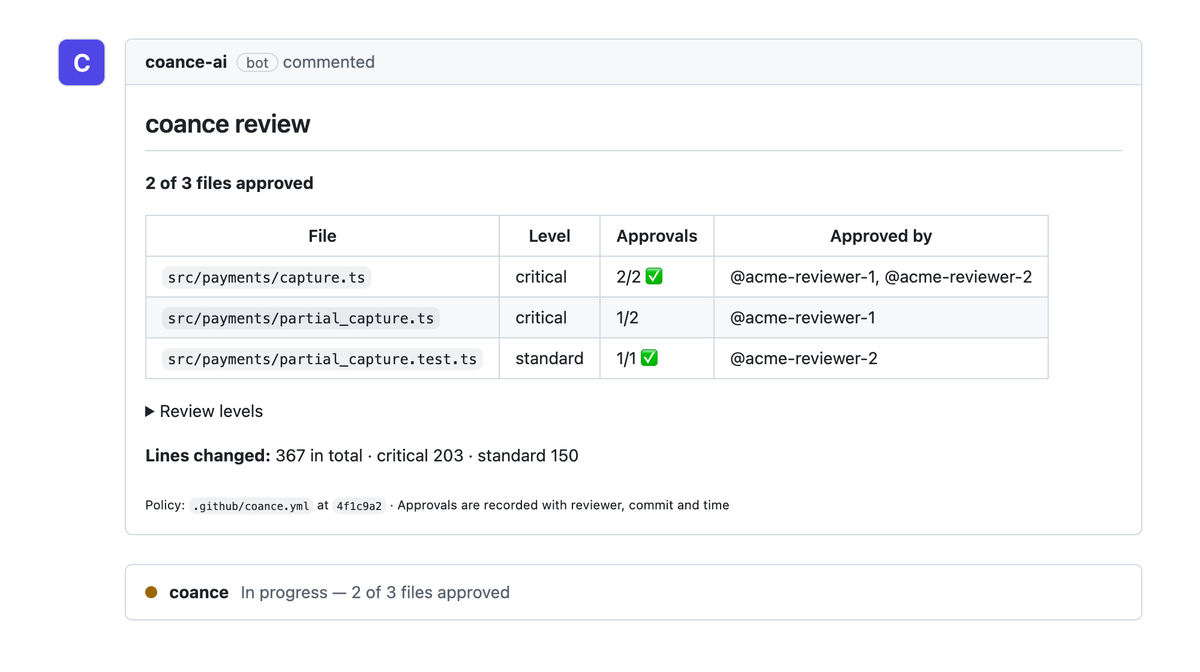
Coance records who approved which file, when and at which commit.
Not every file carries the same risk
AI tools make pull requests larger and more frequent, so review thins out everywhere,
including on payments, access control and migrations. CODEOWNERS says who owns
a path, not how carefully it must be reviewed.
How it works
-
Write the policy
Define review levels and map paths to them in coance.yml or CODEOWNERS.
-
Review file by file
Coance opens a thread on each governed file. Reviewers approve by resolving it or replying /approve.
-
Pass one check
The coance check passes when every governed file has its approvals.
The policy in one file
Payments, authentication, migrations and the policy itself need two approvers, neither of
them the author. The rest of /src/ gets an ordinary review.
Files no rule matches are treated as lower risk and may need less review: Coance adds no requirement for them, and your repository’s usual review process applies.
# .github/coance.yml
levels:
  critical:
    approvals: 2
    self_review: false
    description: |
      Money, access or data that is hard to undo. Read
      every changed line; two reviewers, neither of them
      the author.
  standard:
    description: Read the file. Does the change make sense?

rules:
  critical:
    paths:
      /src/payments/: '@acme/payments @acme/security'
      /src/auth/: '@acme/security'
      /db/migrations/: '@acme/data @acme/security'
      /.github/coance.yml: '@acme/security @acme/leads'
  standard:
    paths: ['/src/']
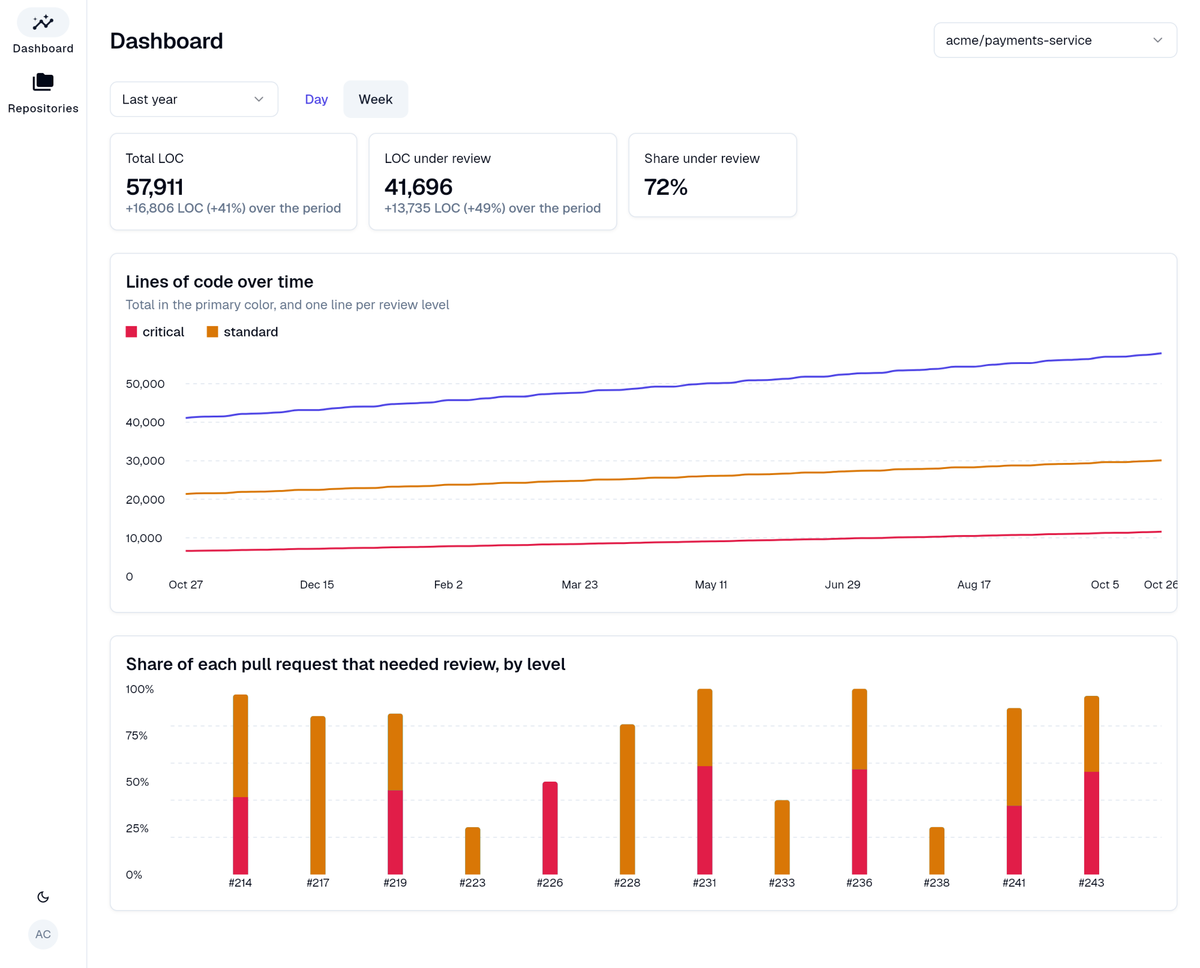
See your code by risk level
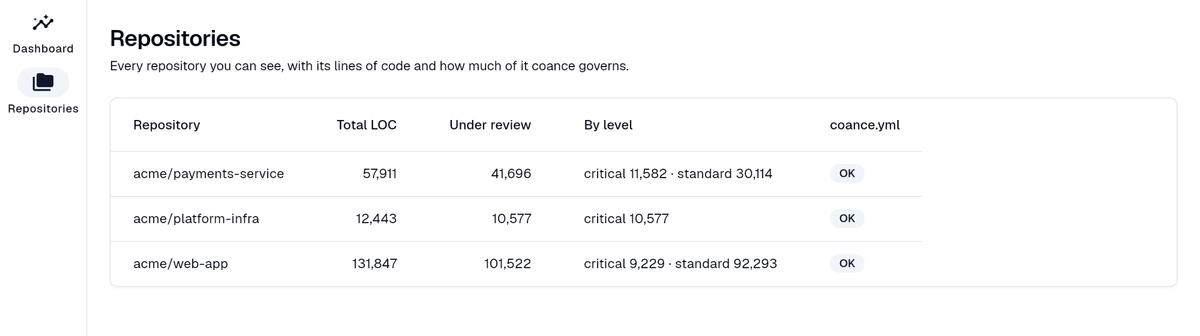
How much code you have, how much sits under each review level (and how much is critical), and how that changes with every merge.
- Total lines of code, and the lines under each review level
- The share of your code governed with Coance
- How these change over time, by day or by week
- The share of each pull request’s changes that needed review under your policy
- Generated and vendored files are excluded from the metrics.
Use cases
Payments
Two reviewers, neither the author.
Health data
Owned by privacy and security.
Auth and cryptography
Approved by the security team.
Infrastructure and CI/CD
Including the review policy itself.
Database migrations
Reviewed by people who know the data.
Generated code
Excluded from Coance’s requirements and metrics.
Regulatory context
Few rules require line-by-line review; many ask for controlled, documented change. PCI DSS asks for custom software to be reviewed before release, by someone other than the author when reviews are manual. [1] NIST’s SSDF leaves it to the organization to decide where code review is used. [2] DORA asks EU financial entities for change management in which changes are recorded, assessed and approved. [5]
Coance helps you demonstrate a documented, enforced and auditable review process. It does not make you compliant with any of these, and this is not legal advice. More context and sources →
Get started
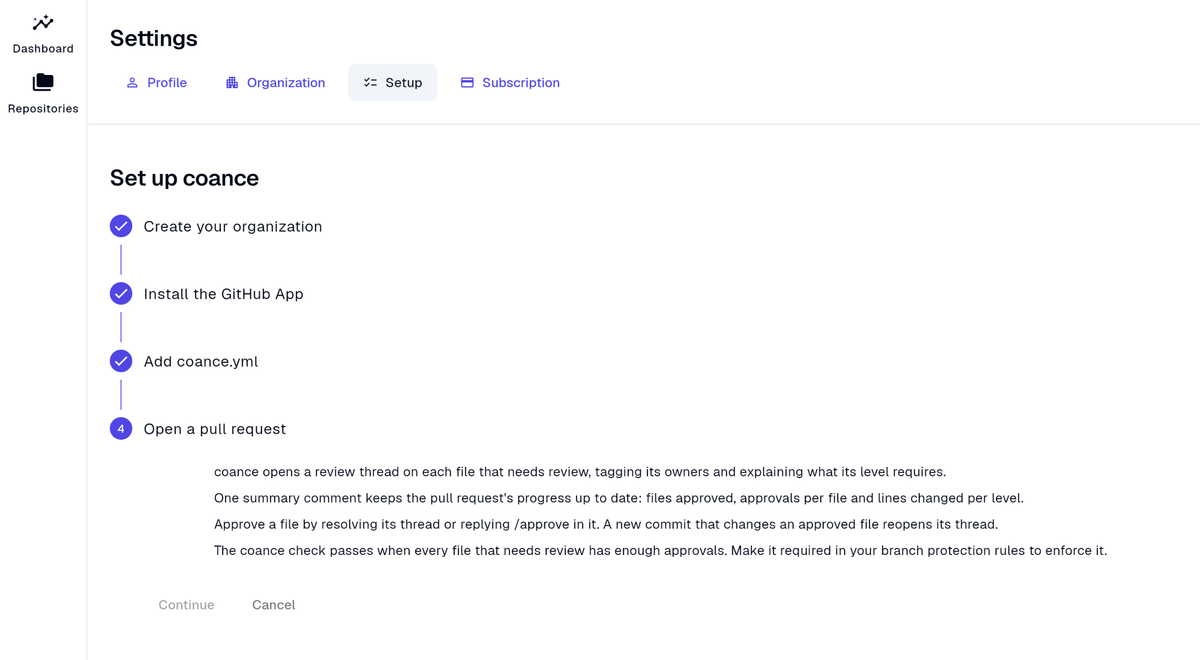
Create your organization, install the GitHub App, add coance.yml and open a
pull request. The app guides you through each step.