 Coance
For teams shipping with AI
Risk-based code review and codebase analytics.
AI delivers whole features at once. Decide which code is critical and who reviews it; Coance applies that to every pull request and shows how much critical code you have and how it changes.
How it works
-
Write the policy
Define review levels and map paths to them in coance.yml or CODEOWNERS.
-
Review files by risk level
Coance asks each file’s owners for the review its level needs. The coance check passes when every governed file is approved.
-
Analyze your code
See the lines of code under each risk level, and how they change over time.
The policy in one file
Files under /src/payments/ are critical: they need two approvers from the
payments or security team, neither of them the author. Add a level for each area that
needs a careful review.
Files no rule matches are treated as lower risk and may need less review: Coance adds no requirement for them, and your repository’s usual review process applies.
# .github/coance.yml
levels:
  critical:
    approvals: 2
    self_review: false
    description: |
      Money moves here. Read every changed line; two
      reviewers, neither the author. Related: PCI DSS
      v4.0.1 requirement 6.2.3.1.

rules:
  critical:
    paths:
      /src/payments/: '@acme/payments @acme/security'
Review files by risk level
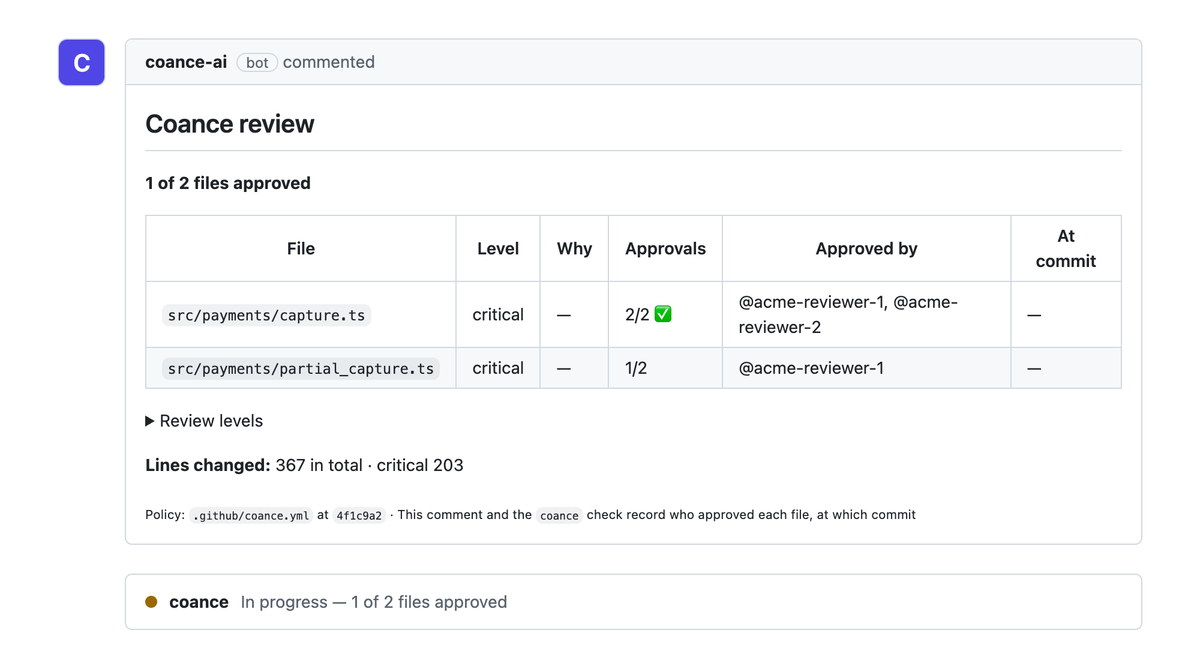
Each governed file gets a thread that tags its owners, who approve it by resolving the
thread or replying /approve. One summary comment tracks the pull request, and
the coance check passes when every governed file is approved.
See your code by risk level
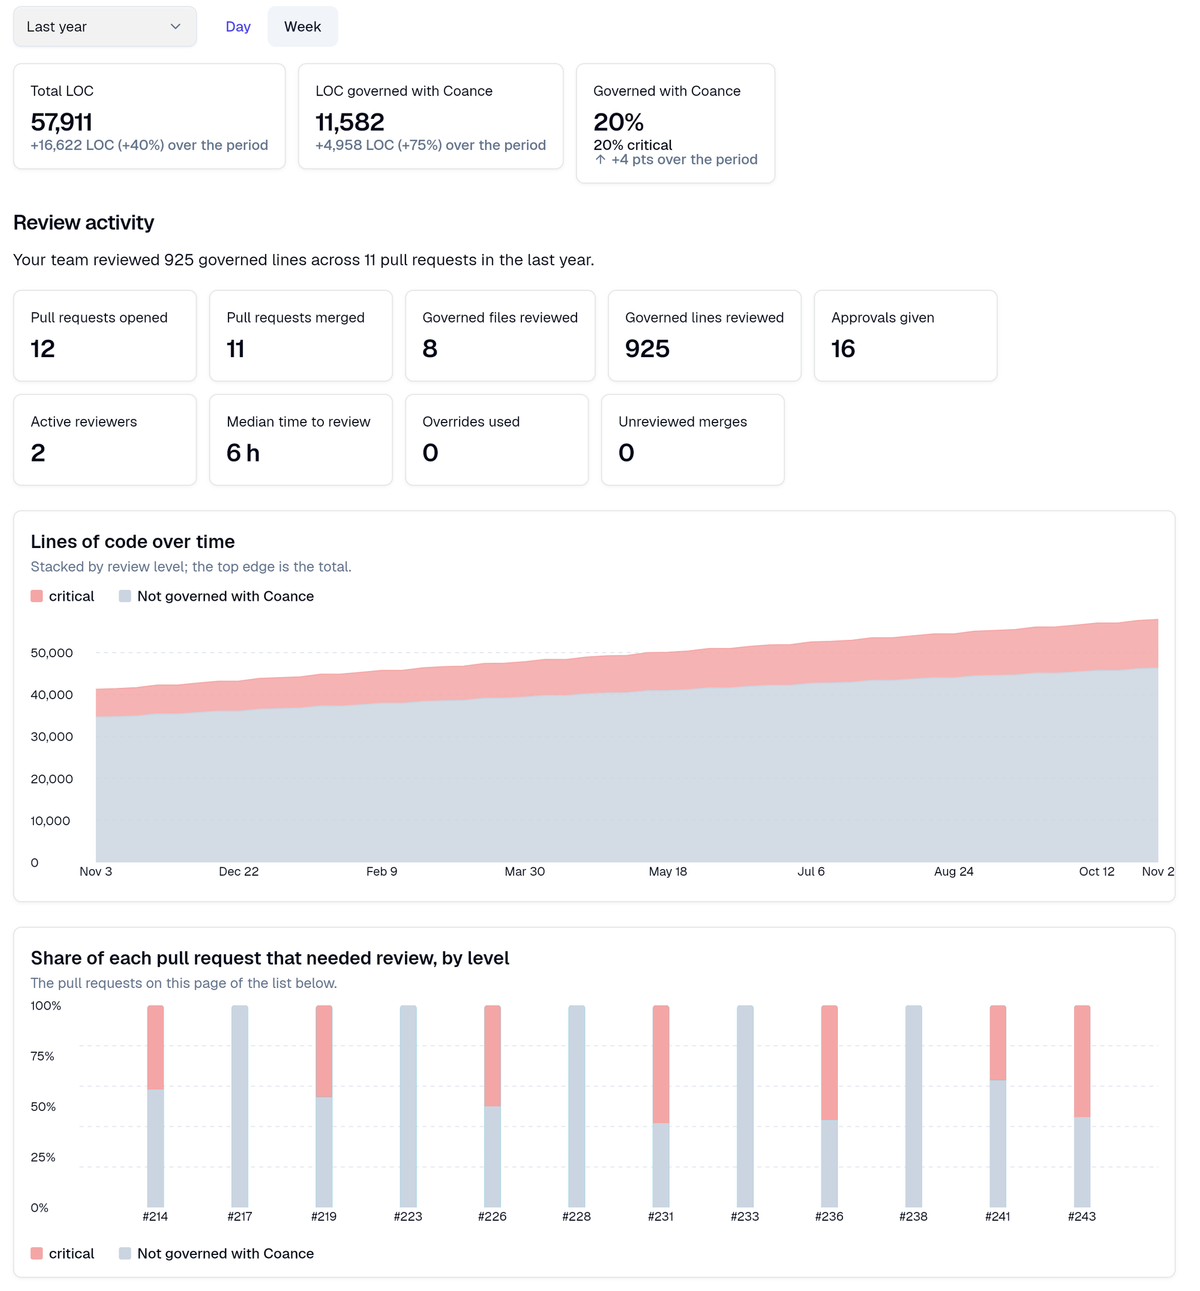
AI makes pull requests larger and more frequent, and review thins out everywhere, payments and access control included. See how much of your code sits under each review level, and how that changes with every merge.
Use cases
Payments
Two reviewers, neither the author.
Health data
Owned by privacy and security.
Auth and cryptography
Approved by the security team.
Infrastructure and CI/CD
Including the review policy itself.
Database migrations
Reviewed by people who know the data.
Generated code
Excluded from Coance’s requirements and metrics.
Regulatory context
Few rules require line-by-line review; many ask for controlled, documented change. PCI DSS asks for custom software to be reviewed before release, by someone other than the author when reviews are manual. [1] NIST’s SSDF leaves it to the organization to decide where code review is used. [2] DORA asks EU financial entities for change management in which changes are recorded, assessed and approved. [5]
Coance helps you demonstrate a documented, enforced and auditable review process. It does not make you compliant with any of these, and this is not legal advice. More context and sources →
Get started
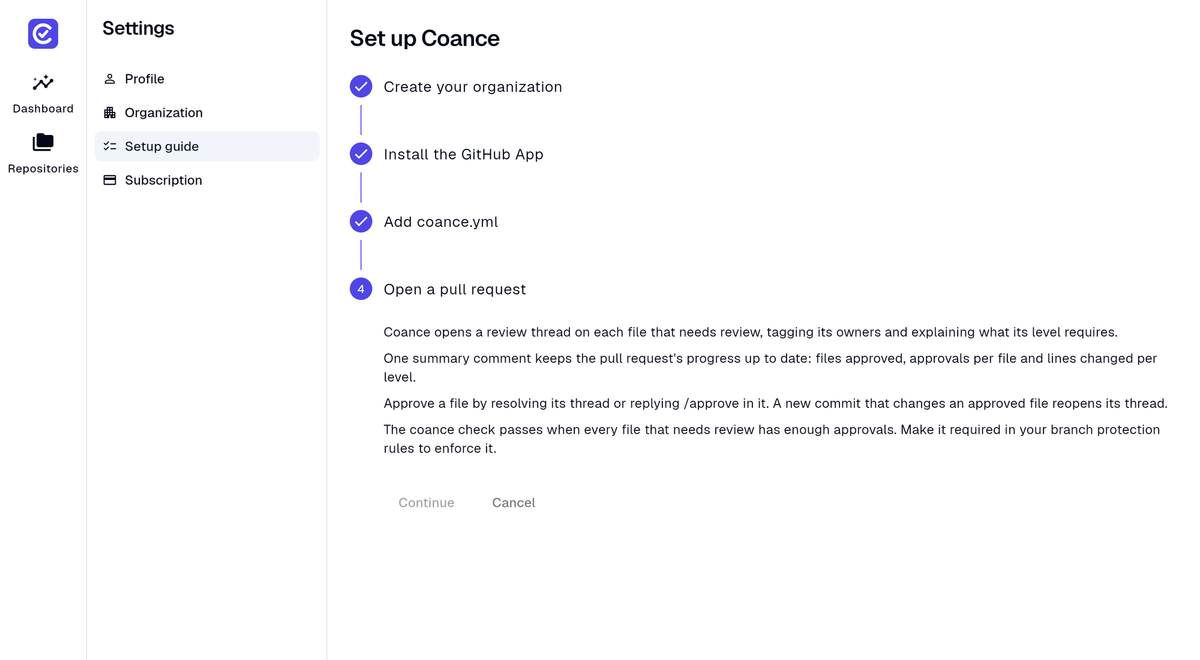
Create your organization, install the GitHub App, add coance.yml and open a
pull request. The app guides you through each step.